HIPAA Risk Assessment Is More Than a Checklist or Scan, DYOPATH Guide Says
Oct 22, 2026
A new DYOPATH guide explains why a checklist, questionnaire, or vulnerability scan falls short of a HIPAA security risk assessment, and what a proper one covers.
Oakbrook Terrace, United States, October 22, 2026 /NewsNetwork/ -- DYOPATH has published a guide to HIPAA security risk assessments (https://dyopath.com/hipaa-security-risk-assessment/), aimed at healthcare organizations that may have completed something they call an assessment without meeting the actual requirement.
Many organizations have done a checklist, a vendor questionnaire, or a firewall check and called it finished. The guide says that doesn’t meet the requirement. Office for Civil Rights audits and breach investigations tend to focus on the difference.
The rule behind it is 45 CFR § 164.308(a)(1)(ii)(A), the risk analysis requirement in the HIPAA Security Rule. It applies to any covered entity or business associate that holds electronic protected health information, whatever its size.
According to the guide, the assessment must extend well beyond the network. It looks at administrative safeguards like training and business associate agreements, physical safeguards like facility access and device disposal, and technical safeguards like access controls and encryption. Scans mostly test that last group, which is why one scan can’t stand in for the whole analysis.
The guide puts the inventory first, meaning where patient data actually lives. It points to backups, fax servers, billing platforms, and texting apps as places that get missed. After that, it scores each risk and tests the controls already in place.
No pass or fail grade comes out of it. The guide describes a prioritized risk register and a remediation plan, and says the Office for Civil Rights often asks for the assessment first in an investigation.
The gaps assessors find most often include patient data nobody tracked, access left open after a role change, and lapsed business associate agreements.
HIPAA has no fixed interval for redoing it. Many organizations review annually, and a merger, a new electronic health record system, or a security incident is reason to reassess sooner.
The larger message is that compliance is ongoing. No assessment, and no vendor, can make healthcare organizations (https://dyopath.com/healthcare-medical/) “HIPAA compliant” as a one-time achievement. Findings need owners, deadlines set by severity, and tracking until they’re closed.
DYOPATH says it has performed assessments against HIPAA, NIST, and related frameworks through its governance, risk, and compliance practice. Organizations that want to discuss a cybersecurity assessment (https://dyopath.com/cyber-security-assessments/) can contact the team.
About DYOPATH:
DYOPATH is a Houston, TX company with roots back to 1996. It delivers managed IT, cybersecurity, and cloud services to organizations across the United States and Mexico, backed by more than 600 U.S.-based professionals. Learn more at https://dyopath.com/about-it-company/.
Contact Info:
Name: Charles Orrico
Email: Send Email
Organization: DYOPATH
Address: 1801 South Meyers Road, Oakbrook Terrace, Illinois 60181, United States
Website: https://dyopath.com/
Source: NewsNetwork
Release ID: 89207035
Should any problems, inaccuracies, or doubts arise from the content contained within this press release, we kindly request that you inform us immediately by contacting [email protected] (it is important to note that this email is the authorized channel for such matters, sending multiple emails to multiple addresses does not necessarily help expedite your request). Our dedicated team will promptly address your concerns within 8 hours, taking necessary steps to rectify identified issues or assist with the removal process. Providing accurate and dependable information is at the core of our commitment to our readers.
Recommended




YOUR NEWS, OUR NETWORK.
Do you have Great News you want to tell the world?
Be it updates about your business or your community, you can make sure that it’s heard by submitting your story to our network reaching hundreds of news sites across 6 verticals.
More News

Unseen pictures of 1930s from Manchester's Ritz to Rochdale 'Riviera'
From Rochdale's lost "Norden Riviera" lido to an almost deserted East Lancashire Road, a remarkable new book featuring 600 unseen 1930s archive photographs captures Greater Manchester on the brink of WWII.
ASX rebounds to end on a high; CSL names new chair
The Australian sharemarket has rebounded after an early fall to close in the green, with materials and energy stocks posting gains.

Hoover rivalling Dyson and Shark gets huge £69 price drop with clever deal
"It performs far better than I expected and feels like a much more expensive machine than it actually is"

Shocking CCTV footage shows daycare centre worker assaulting child
Disturbing CCTV footage has captured a childcare worker kicking, slapping and shaking three little boys during more than 80 assaults while they were in her care.

Philadelphia police officer shot 12 times after he and his partner were ambushed released from hospital two weeks after horrifying attack
A huge crowd of medical staff, law enforcement and members of the community stood outside the hospital clapping and cheering as the officer was released.
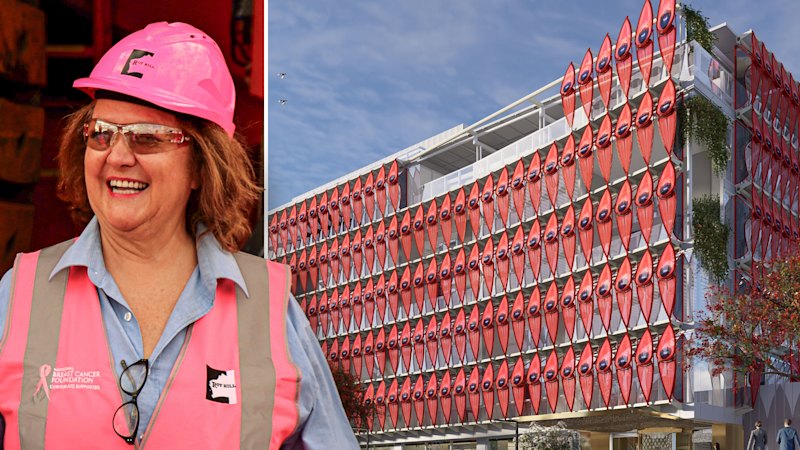
Gina Rinehart takes fight for helipad at Hancock’s Perth HQ to tribunal
Gina Rinehart’s company Hancock Prospecting has taken its fight to build a helipad atop its West Perth headquarters to the State Administrative Tribunal after it was knocked back by the local council.

Coronation Street star warns of 'devastated' Carla Connor-Swain scenes as past trauma triggered
Carla Connor-Swain will be left 'devastated' in upcoming scenes as she's forced to face that the Underworld factory may be no more
Tassie, Vic gold output clears Kaiser Reef debt as cash hits $40M
Kaiser Reef produced 6263oz of gold, lifting cash to $40m, clearing its Henty acquisition loan in Tasmania and advancing underground drilling at Maldon in Victoria.

STR, Sara: Total aid the same in 2027, but less cash for low-income families
For families earning below RM2.5k, cash handout reduced by up to RM600, while Sara raised to RM1.8k.

Confused passengers arrive at Australia's newest airport as traveller admits: 'I'm meant to be in Perth'
The landmark opening took an awkward turn when one man arriving from Auckland on an Air New Zealand flight admitted he had intended to travel to Perth.

Marks and Spencer's £26 Christmas party dress in two sparkly colours is 'comfy and flattering'
"So comfortable to wear. My figure isn’t traditionally shapely but this dress doesn’t care about that - it fits and it’s lovely."

Coronation Street spoilers with Carla's sad decision, Gary's prison drama and Ronnie's heartbreak
There's also drama between Daniel and Adam next week in the ITV soap, while Gemma gets her results